Compliance
When a customer, insurer or assessor asks how you protect information, you need answers backed by your systems. Our compliance support connects technical controls with the evidence behind them, helping you understand where you stand and what needs attention.
How we help
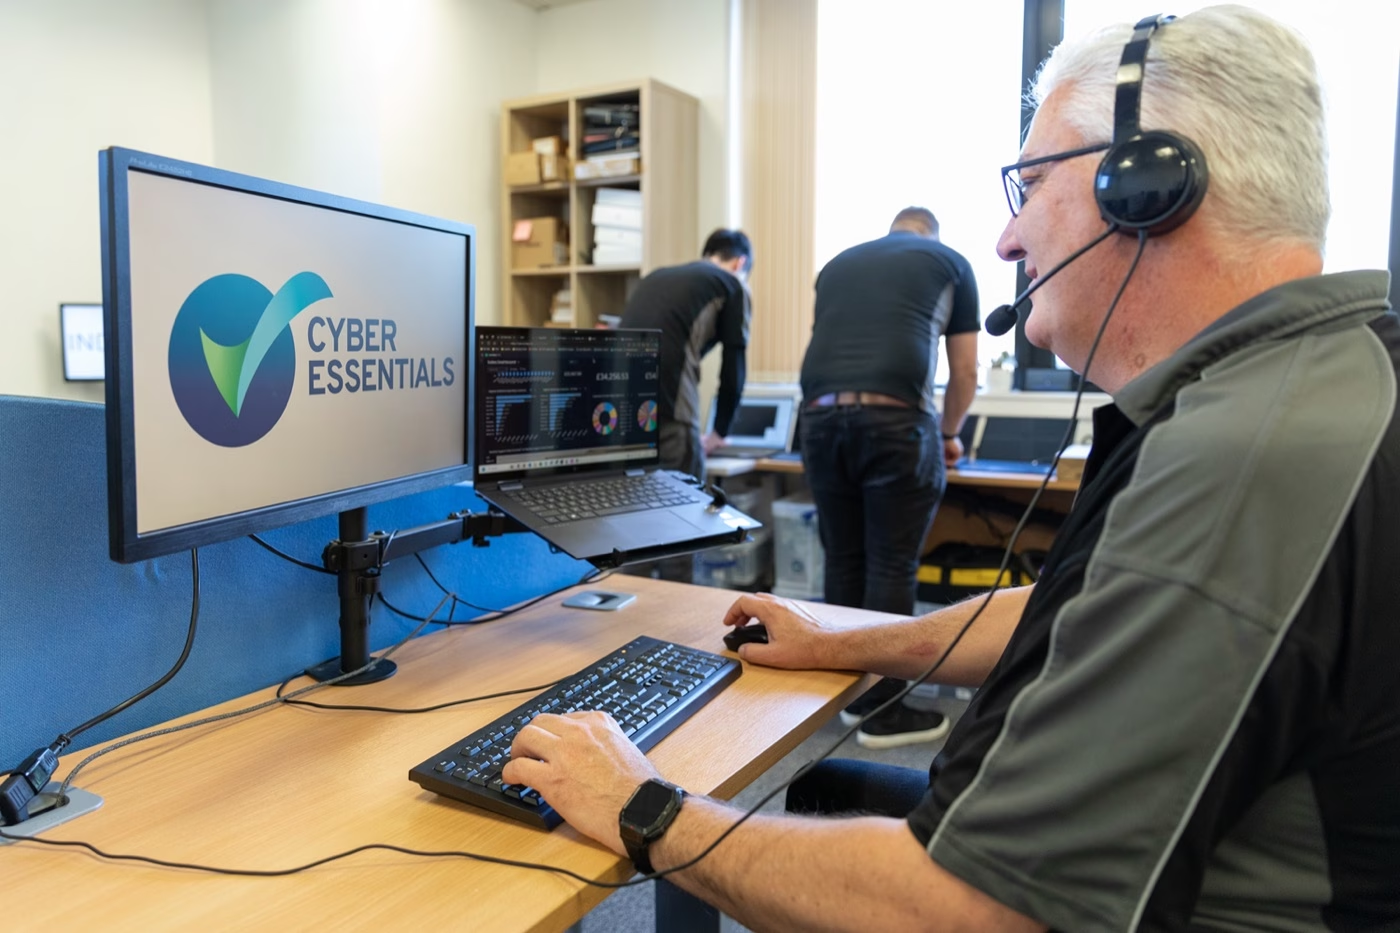
We help assess your Cyber Essentials readiness, address gaps and prepare for independent assessment. For example, that may mean reviewing device settings and removing unnecessary administrator access before you apply. INDIGO IT holds Cyber Essentials Plus; your assessment body makes the certification decision.
Cyber Essentials supportA policy is more useful when the systems behind it support what it says. We review technical weaknesses such as old accounts or missing updates, explain their significance and help prioritise the fixes. That gives you practical actions alongside the documents you're asked to maintain.
A customer questionnaire may ask for evidence that several people or suppliers hold. We help organise the technical information, such as account settings, backup records and update processes, so you can answer accurately. Keeping that evidence connected to your current setup makes future reviews easier to prepare for.
A new customer, application or working arrangement can change the evidence your business needs. We review the technical implications and help identify controls that need attention. For example, moving files into a shared cloud workspace should prompt a review of who can see them and how access is managed.
Monitoring and mapping
A useful review starts with the requirement itself and the devices, accounts and applications it applies to. We look at what the available technical evidence shows, where there are gaps and which findings need investigation. This gives you a clearer basis for deciding what needs to change.
Our monitoring tools support continuous checks of the managed IT environment, with findings mapped against relevant technical requirements. Alerts can highlight changes that need attention, while the review connects those findings with the actions and evidence required.
For example, a requirement to control access needs more than a statement that permissions are reviewed. The supporting work includes checking actual accounts, removing access when someone leaves and recording the review. Technical checks can support that process, while policy decisions and approval responsibilities remain part of running your business.
By sector
You may face GDPR responsibilities alongside customer requests for Cyber Essentials or ISO 27001 assurance. PCI-DSS is relevant where your work brings payment-card data into scope. We start by clarifying the requirement and the technical evidence needed, including access controls, device protection and recovery arrangements.
Sensitive records make access, device security and continuity important parts of daily operations. Your business may also need evidence relating to CQC expectations and NHS data standards, including the Data Security and Protection Toolkit where applicable. The technical work should follow the actual scope of your services and the requirements you've been given.
Confidential client information needs appropriate controls across accounts, devices and shared files. SRA requirements and GDPR responsibilities may sit alongside customer requests for Cyber Essentials or other security evidence. We help clarify the IT controls behind those questions, including who has access and how that access changes when people leave.
Client feedback
“The Indigo Team have been supporting Roast & Ground for all things IT related for many years. They are knowledgeable, responsive and great to work with. Highly recommend.”
Catherine Gray · Trustpilot review

Making great IT personal and accessible
Matt is passionate about technology and helping businesses to thrive with it. If your tech is in a tangle, he'd love to help you. Whether it's tricky tech, cyber security, or transforming your business's IT to achieve your goals, Matt can offer clear guidance, free from the technobabble.
Ready to make headway to exceptional IT? It all starts with an informal conversation!
Frequently asked questions
If yours isn't here, call us on 01491 693424.
Cyber Essentials assesses a defined set of technical controls, while ISO 27001 covers an information security management system. Which you need depends on the risks and requirements you are addressing; our framework comparison explains the distinction.
We help with Cyber Essentials and Cyber Essentials Plus preparation, including reviewing controls and addressing gaps. The independent certification body assesses your application; INDIGO IT holds Cyber Essentials Plus itself.
Bring the request you've received, the deadline and any existing policies or technical evidence. Knowing who is asking and what systems are in scope helps us explain the IT work involved.
Monitoring helps identify technical gaps and changes, but compliance also involves people, processes and the requirements that apply to your work. We explain what the IT evidence can demonstrate and where your business needs further action or specialist input.